The Model Context Protocol has become a standard route between AI agents and external tools, but its rapid adoption is creating a security gap that conventional defenses were not designed to close.
Anthropic introduced MCP as an open standard in November 2024. By December 2025, the company said more than 10,000 active public MCP servers were operating, supported by AWS, Google Cloud, Azure and other providers. Major AI platforms and coding assistants including ChatGPT, Gemini, Microsoft Copilot, Cursor and Visual Studio Code now use the protocol.
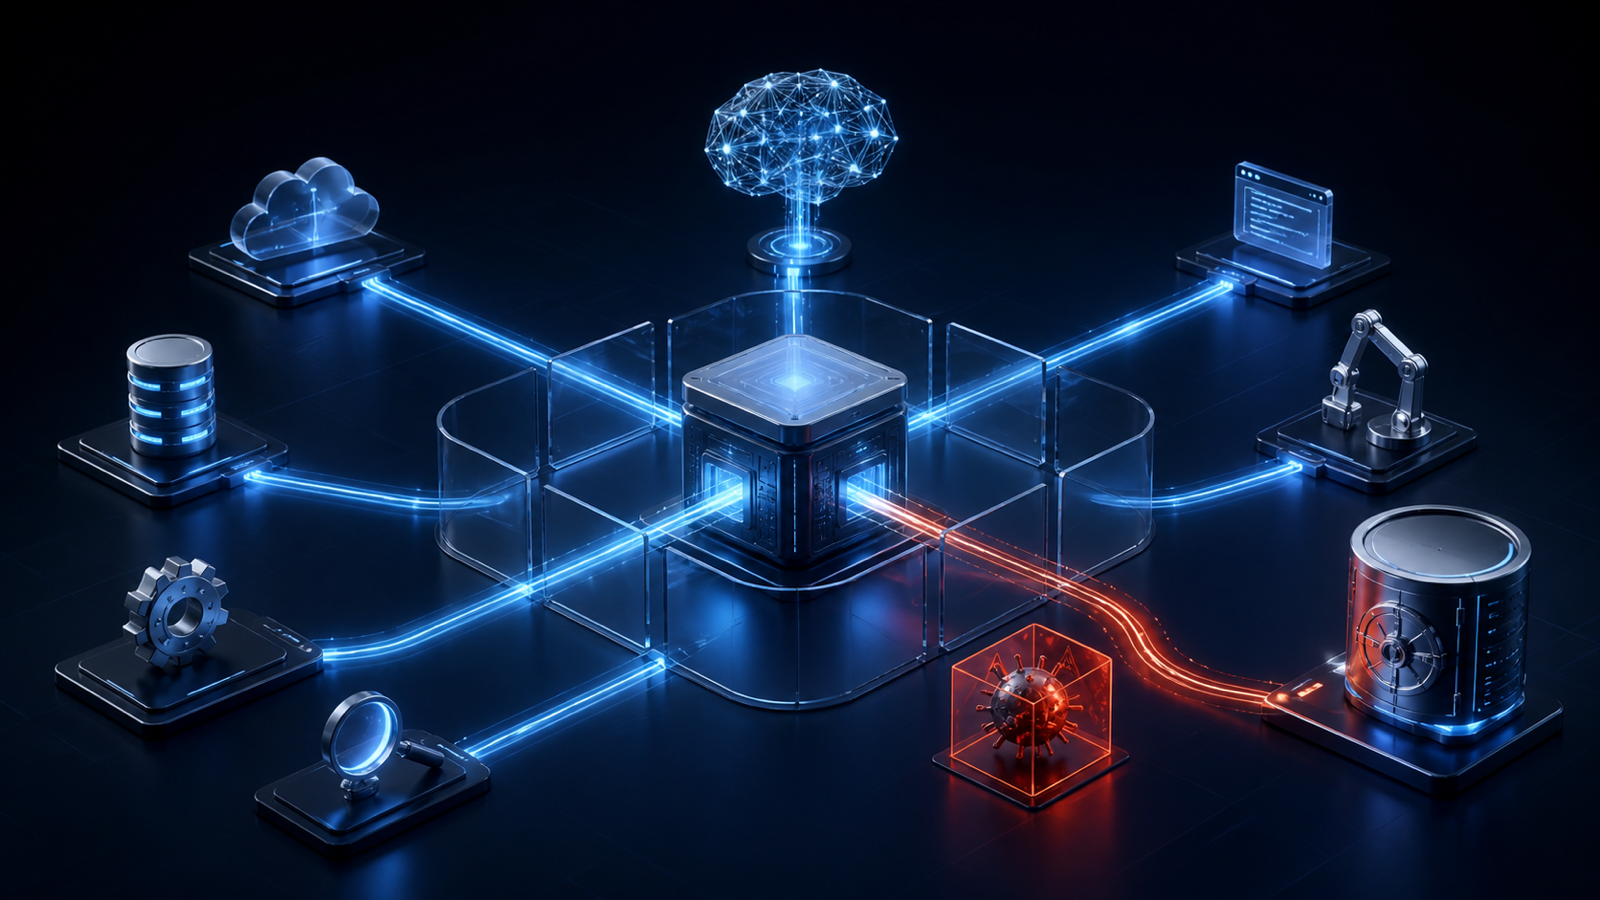
That reach makes MCP useful: one interface can connect an agent, assistant or coding tool with multiple data sources and applications instead of requiring a separate connector for each. It also gives attackers a common path into systems where AI can take actions with real permissions.
Tool descriptions can become instructions for attack
The Open Worldwide Application Security Project identifies tool poisoning as a central MCP threat. An attacker can place malicious instructions inside a tool description, schema or returned result, turning prompt injection into a mechanism for manipulating agent behavior.
Other attacks exploit the trust created when a user approves a tool. In a rug pull, the tool’s definition changes after approval. Tool shadowing and cross-origin escalation use a malicious server’s description to influence how an agent handles a separate, trusted tool.
The scale of reported weakness is substantial. Lakera, an AI security company acquired by Check Point in 2025, analyzed 10,000 MCP servers and found exploitable weaknesses in 40%, according to research cited by AI News. That is a vendor-linked analysis rather than a complete census of every server, but it indicates that the risk is not limited to unusual experiments.
MCP can also support more familiar forms of data theft. Sensitive information may be inserted covertly into apparently legitimate actions such as searches or emails. A server granted broader access than a task requires creates another opening, because the agent can reach more data or systems if the connector is compromised.
Protecting MCP does not secure every agent path
Securing MCP servers can reduce tool poisoning, unauthorized access and data leakage, but the protocol is only one way for agents to interact with outside systems. An agent may call other interfaces that bypass MCP entirely.
That distinction matters when companies evaluate products described as “AI firewalls.” The phrase currently covers two different categories. One is a conventional firewall enhanced by AI to detect malware or intrusion. The newer category is designed to protect AI models, agents and connected tools from prompt injection, unsafe behavior and information leakage.
An MCP-focused control therefore needs to be assessed within a larger security architecture. It can inspect a specific connection without governing every route an agent may use. Organizations must consider how that product integrates with access management, network controls and other safeguards across the AI environment.
The speed of MCP adoption makes this coordination harder. The protocol spread broadly in roughly a year, while security teams and vendors are still defining how responsibility should be divided between an agent, a connector and the network carrying its traffic.
Vendors are testing different control points
Several suppliers are approaching the gap from different layers. TrueFoundry’s AI Gateway offers infrastructure-level governance, access controls and auditing for interactions between agents and MCP tools. Cisco has expanded AI Defense with agent guardrails, MCP scanning and real-time inspection intended to detect unsafe behavior.
Check Point released its AI Network Firewall in July 2026. Its network-centered approach discovers MCP servers, inspects their traffic and applies policies to agent access while also covering other connections between AI systems, employees and external data.
These are vendor descriptions of product capabilities, not evidence in the source that one method prevents every listed attack. Infrastructure governance can control approved connections, dedicated guardrails can examine agent behavior, and network inspection can observe traffic, but each operates at a different point.
The immediate issue is less which label wins than whether organizations can see the tools their agents use, limit permissions and detect when approved behavior changes. MCP standardizes connectivity; it does not automatically standardize trust.
As agents gain access to email, search, code and sensitive records, a compromised connector can translate model manipulation into external action. The protocol’s success has made MCP security an operational requirement sooner than many teams expected, while the wider agent ecosystem still demands controls beyond MCP itself.